Appearance
API keys
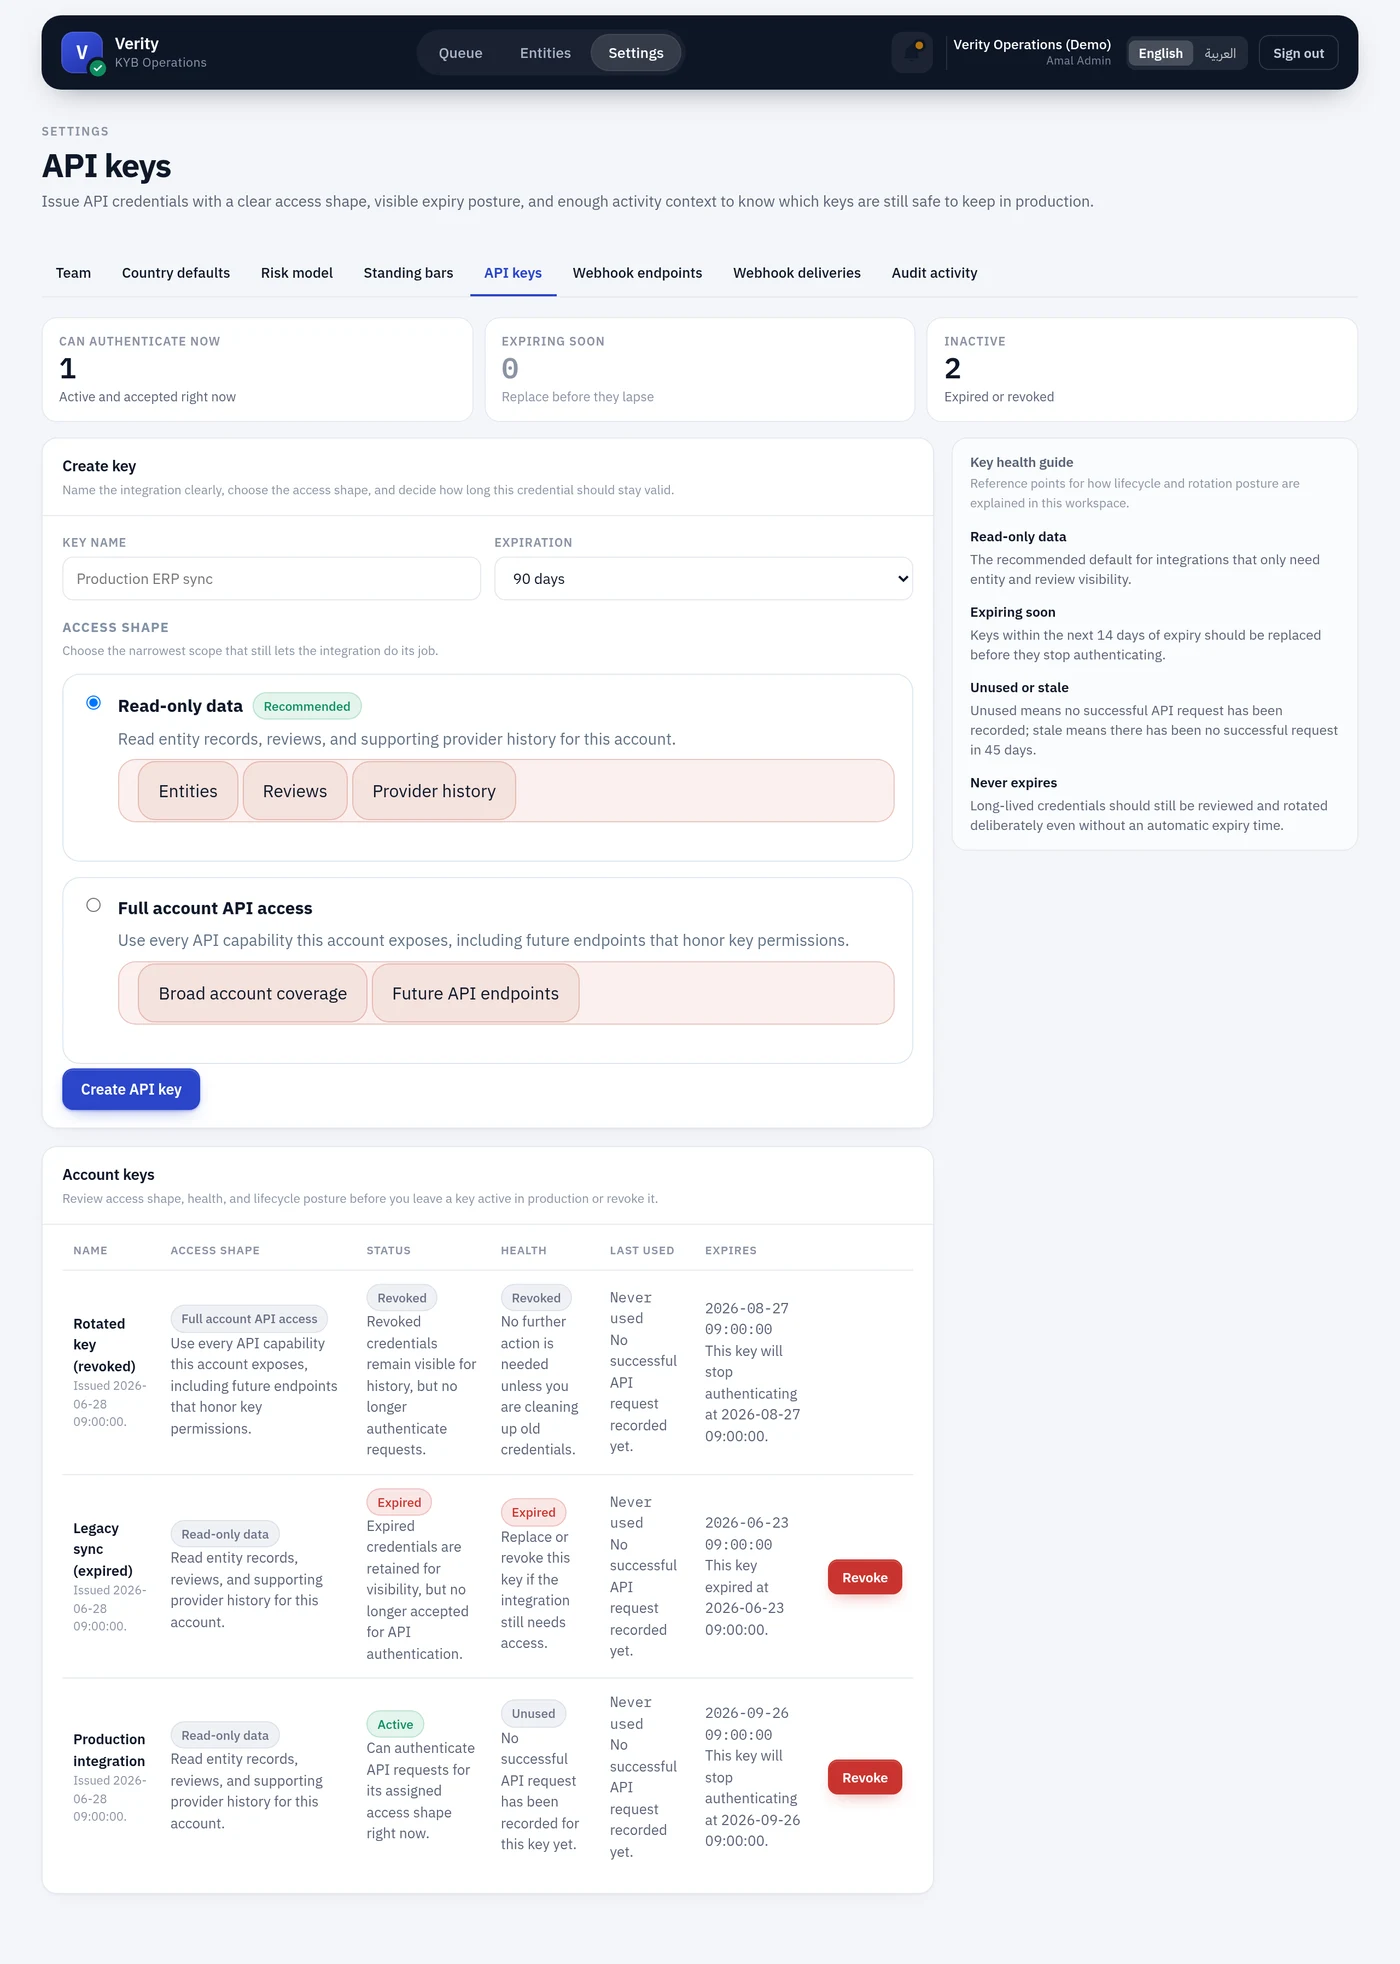
Settings → API keys, needing api_key.manage. See Authentication for how they are used.
Issuing
Provide a name, a scope and an expiry policy. The raw token is shown once. Verity stores only a SHA-256 digest and cannot recover it.
Name keys after the integration that will hold them, not after a person — the point of the name is knowing what breaks when you revoke it.
Lifecycle signals
| Signal | When |
|---|---|
| Expiring soon | Within 14 days of expiry |
| Stale | Not used for 45 days |
| Rotation recommended | Older than 180 days |
A stale key is worth attention: either something stopped using it, or nothing ever did.
Revoking
Immediate. The next request with that token gets 401. Issue and revoke are both audited (api_key.created, api_key.revoked).
Practices worth keeping
- One key per integration, so revocation is surgical
account_readunless a write is genuinely needed- Store in a secret manager, never in source control
- Rotate deliberately, rather than discovering expiry in production